Skip to content

Add hacker issue reporting - #595

Merged
DVidal1205 merged 8 commits into
mainfrom
2026/hacker-issue-reporting-config
Oct 5, 2026
Merged

DVidal1205 merged 8 commits into
mainfrom
2026/hacker-issue-reporting-config

Conversation

@alexanderpaolini

Copy link
Copy Markdown
Contributor

Why

There was a "Report Issue" button on the hacker dashboard that doesn't do anything. Currently it copies the issue and links the hacker to the Discord server.

What

This change adds hackathon issue reports channel and role to ping to the Hackathon table. When hackers report issues, a message is sent to that channel, and the role is pinged. Rate limits are set to 5 reports in 10 minutes.

Test Plan

Tested everything except sending a real notification. Code LGTM, which is why I'm making this PR.

Checklist

  • Database: No schema changes, OR I ran pnpm db:generate and committed the generated files in packages/db/drizzle/
  • Environment Variables: No environment variables changed, OR I have contacted the Development Lead to modify them on Coolify BEFORE merging.

@coderabbitai coderabbitai Bot left a comment

Copy link
Copy Markdown

Choose a reason for hiding this comment

The reason will be displayed to describe this comment to others. Learn more.

Actionable comments posted: 1

🧹 Nitpick comments (1)
apps/blade/src/app/_components/admin/hackathon/issue-reporting-section.tsx (1)

26-27: 📐 Maintainability & Code Quality | 🔵 Trivial | ⚡ Quick win

Pass issue-reporting settings through RSC props.

Add issueReportsChannelId and issueReportsRoleId to HACKATHON_COLUMNS. Pass them through detail to IssueReportingSection, use the parent’s onSaved={refresh}, and remove the client query, invalidation, and loading/error branches.


ℹ️ Review info
⚙️ Run configuration
  • Configuration used: Repository: KnightHacks/forge/.coderabbit.yml
  • Review profile: QUIET
  • Plan: Advanced
  • Run ID: df9c021b-f50c-40a4-aed2-12b1b513c2d2
📥 Commits

Reviewing files that changed from the base of the PR and between 6be7b95 and 2ca62cb.

📒 Files selected for processing (25)
  • .forge/features/hacker-issue-reporting/spec.md
  • .forge/features/hacker-issue-reporting/srd.md
  • .forge/features/hacker-issue-reporting/status.md
  • .forge/features/hacker-issue-reporting/test-cases.md
  • apps/2026/src/app/(portal)/_components/khix-dashboard.tsx
  • apps/2026/src/lib/hacker-portal.tsx
  • apps/blade/src/app/_components/admin/hackathon/hackathon-detail.tsx
  • apps/blade/src/app/_components/admin/hackathon/issue-reporting-section.tsx
  • apps/blade/src/tests/admin/issue-reporting-section.test.tsx
  • packages/api/src/hacker-portal/reports.ts
  • packages/api/src/hacker-portal/router.ts
  • packages/api/src/routers/hackathon.ts
  • packages/api/src/tests/hacker-portal/reports.test.ts
  • packages/api/src/tests/integration/hackathon-portal-configuration.test.ts
  • packages/db/drizzle/0059_melted_squadron_sinister.sql
  • packages/db/drizzle/meta/0059_snapshot.json
  • packages/db/drizzle/meta/_journal.json
  • packages/db/src/schemas/knight-hacks.ts
  • packages/hacker-sdk/README.md
  • packages/hacker-sdk/src/contracts.ts
  • packages/hacker-sdk/src/tests/contracts.test.ts
  • packages/validators/src/audit.ts
  • packages/validators/src/hackathon-portal-admin.ts
  • packages/validators/src/hacker-portal.ts
  • packages/validators/src/tests/hacker-portal.test.ts

Included review availability: This review used your included allowance. Your plan provides up to 1 included review per hour; 0 remain after this review.


Comment thread packages/api/src/hacker-portal/reports.ts Outdated
@KnightHacks KnightHacks deleted a comment from coderabbitai Bot Oct 5, 2026
alexanderpaolini and others added 4 commits October 5, 2026 16:29
Co-authored-by: Codex <codex@openai.com>
@DVidal1205

Copy link
Copy Markdown
Contributor

Addressed the review and KHIX dry-run feedback:

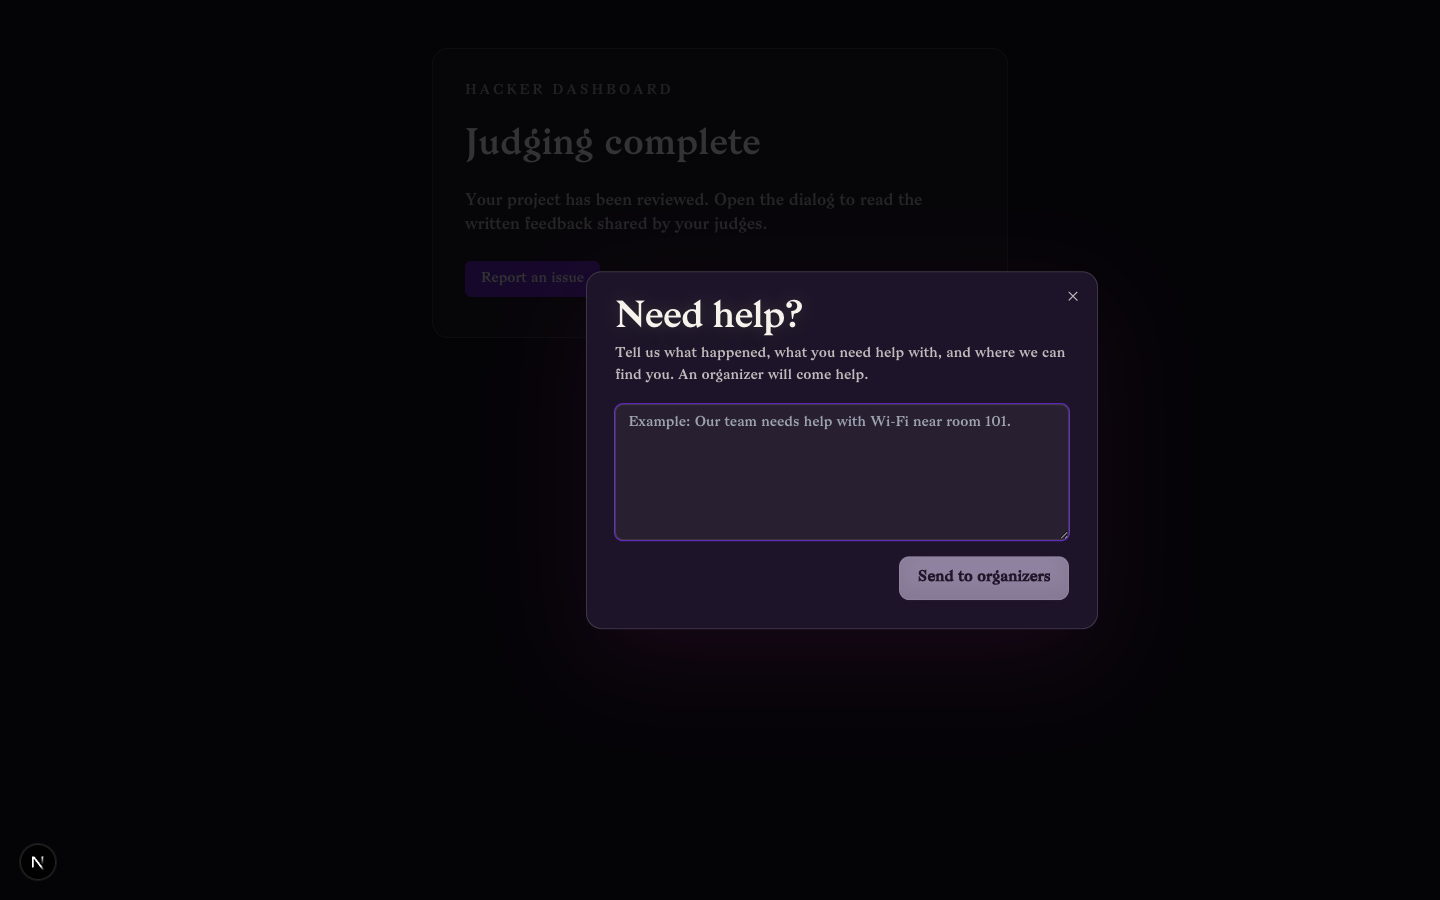
  • The help dialog now asks what happened, what help is needed, and where to find the hacker, without adding another field.
  • Removed the “Prepare for” rubric-item lists from the judging screen.
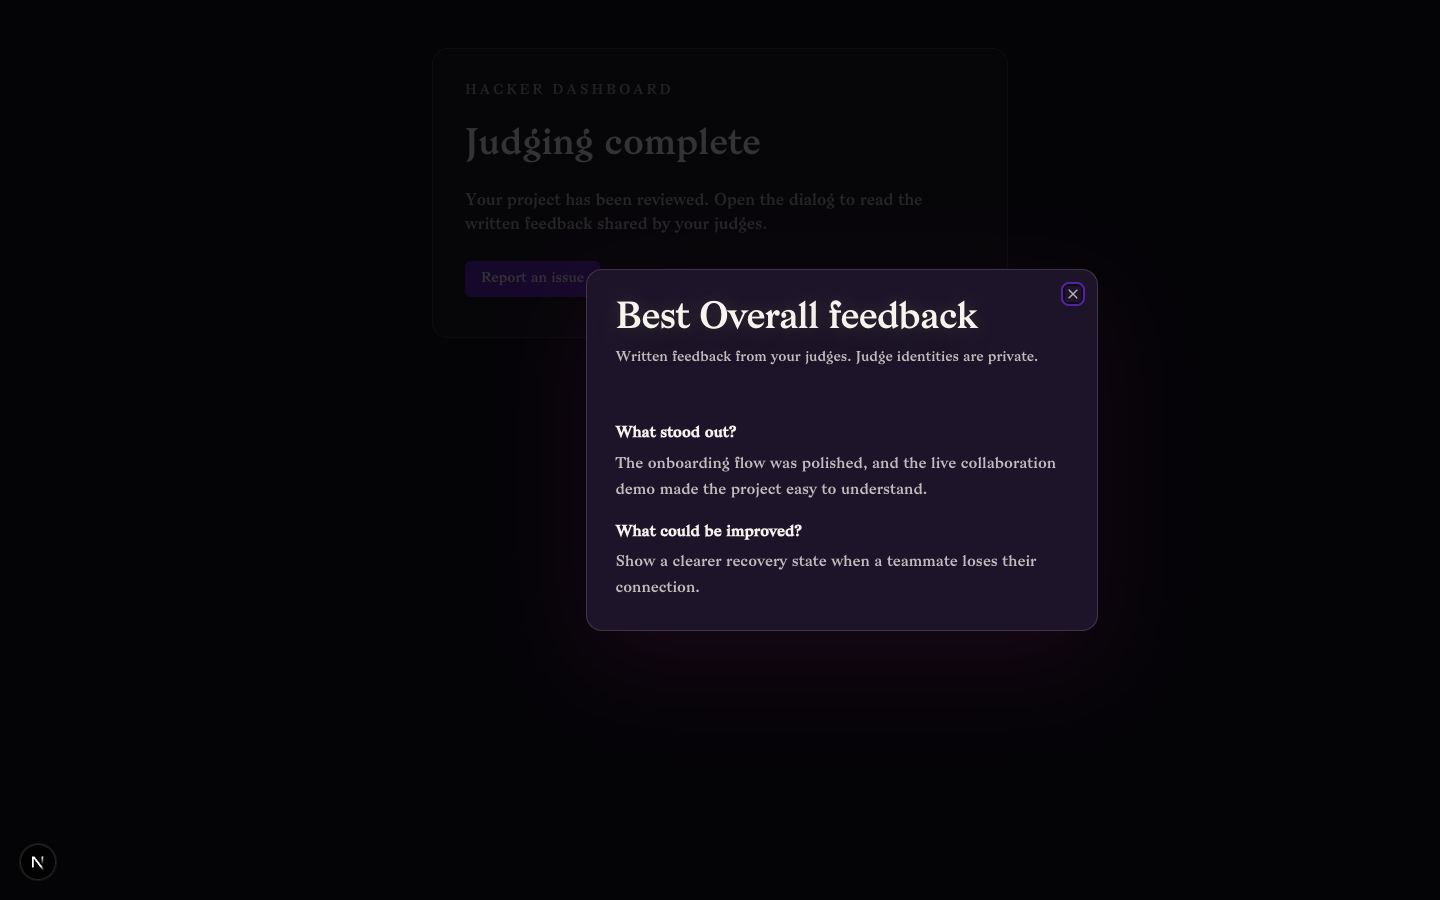
  • Hacker judging feedback now exposes written free-response comments only. Numeric rubric ratings are removed from both the API contract and UI.
  • Moved Discord delivery outside the report transaction and resolved the CodeRabbit thread.
  • Updated the API access, audit, and surface coverage that had been failing CI.

Validation: pnpm verify:precommit; API suite 135 files / 1,087 tests; KHIX suite 11 files / 192 tests. All passed locally.

UI screenshots

Representative local fixture data, rendered with the production KHIX components at 1440 × 900.

Actionable help dialog

Actionable KHIX help dialog

Written-only judging feedback

KHIX written-only judging feedback

Merch pricing remains an organizer-wide follow-up based on the final points table; no code change was made for that item.

Co-authored-by: Codex <codex@openai.com>
@coderabbitai

coderabbitai Bot commented Oct 5, 2026 •

Copy link
Copy Markdown

Review in Change Stack →

Navigate logical layers of code changes, visualize relationships, and explore their blast radius.

No actionable comments were generated in the recent review. 🎉

ℹ️ Recent review info
⚙️ Run configuration
  • Configuration used: Repository: KnightHacks/forge/.coderabbit.yml
  • Review profile: QUIET
  • Plan: Advanced
  • Run ID: e378698c-5cfe-4034-90cf-f35fb8cb3624
📥 Commits

Reviewing files that changed from the base of the PR and between 2ca62cb and c03acdc.

⛔ Files ignored due to path filters (3)
  • .forge/features/hacker-issue-reporting/evidence/issue-help-dialog.png is excluded by !**/*.png
  • .forge/features/hacker-issue-reporting/evidence/written-feedback-dialog.png is excluded by !**/*.png
  • packages/api/src/tests/root/__snapshots__/api-surface.test.ts.snap is excluded by !**/*.snap
📒 Files selected for processing (31)
  • .forge/features/hacker-issue-reporting/evidence/README.md
  • .forge/features/hacker-issue-reporting/srd.md
  • .forge/features/hacker-issue-reporting/status.md
  • .forge/features/hacker-issue-reporting/test-cases.md
  • apps/2026/src/app/(portal)/_components/hacker-judging.module.css
  • apps/2026/src/app/(portal)/_components/hacker-judging.tsx
  • apps/2026/src/app/(portal)/_components/khix-dashboard.tsx
  • apps/2026/src/lib/hacker-portal.tsx
  • apps/blade/src/app/_components/admin/hackathon/hackathon-detail.tsx
  • apps/blade/src/app/_components/admin/hackathon/issue-reporting-section.tsx
  • apps/blade/src/tests/admin/issue-reporting-section.test.tsx
  • packages/api/src/hacker-portal/reports.ts
  • packages/api/src/hacker-portal/router.ts
  • packages/api/src/routers/hackathon.ts
  • packages/api/src/tests/hackathon/access.test.ts
  • packages/api/src/tests/hacker-portal/reports.test.ts
  • packages/api/src/tests/integration/hackathon-portal-configuration.test.ts
  • packages/api/src/tests/integration/project-claims.test.ts
  • packages/api/src/utils/audit/coverage.ts
  • packages/api/src/utils/project-claims/itinerary.ts
  • packages/db/drizzle/0060_early_meteorite.sql
  • packages/db/drizzle/meta/0060_snapshot.json
  • packages/db/drizzle/meta/_journal.json
  • packages/db/src/schemas/knight-hacks.ts
  • packages/db/src/tests/migration-lineage.test.ts
  • packages/hacker-sdk/src/contracts.ts
  • packages/hacker-sdk/src/tests/contracts.test.ts
  • packages/validators/src/audit.ts
  • packages/validators/src/hacker-portal.ts
  • packages/validators/src/project-claims.ts
  • packages/validators/src/tests/hacker-portal.test.ts
💤 Files with no reviewable changes (3)
  • packages/db/drizzle/0060_early_meteorite.sql
  • packages/validators/src/project-claims.ts
  • apps/2026/src/app/(portal)/_components/hacker-judging.module.css

Included review availability: This review used your included allowance. Your plan provides up to 1 included review per hour; 0 remain after this review.


📝 Walkthrough

Walkthrough

Adds officer-managed Discord destinations and a participant API for submitting issue reports. The report flow uses server-derived identity, idempotency, a per-user rate limit, and restricted role mentions. The participant dialog now submits reports to organizers. Judging feedback no longer includes numeric ratings or entries without written responses.

Priority: ⬇️ Low

Merge Risk: ⚪ Minimal · up to c5770

The change adds Discord-backed issue reporting and written-only judging feedback, and no concrete merge-blocking problem was found. One small behavior to be aware of is that failed Discord deliveries count toward the five-reports-per-ten-minutes limit.

Security Architecture Review

Security architecture risk: 🔵 Low · up to c03ac

Reporting is restricted to signed-in applicants and organizer-configured destinations, with controlled mentions and transaction-backed submission limits. Remaining uncertainty concerns delayed delivery retries and deployed Discord permissions. Judging feedback removes scores rather than expanding access to participant data.

Retained concerns
No architecture-level concerns identified.

Security review details

Security Blast Radius

  • inferred — A signed-in applicant can cause the shared bot to send their report and account identifiers to the channel configured for their portal client's hackathon. An officer can configure destinations across hackathons. Actual channel confidentiality and the bot's maximum accessible scope depend on deployed Discord permissions, which were not verified.

Trust Boundaries and Controls

  • observed — The participant procedure requires an enabled portal client and authenticated session. Token lookup is bound to the selected client, while the handler checks the authenticated user's application for that client's hackathon. Request input does not choose user or event identity.
  • observed — Destination changes require a protected session and IS_OFFICER loaded from database role memberships. Permission maps default to false and grant a key only when an assigned role has its corresponding bit set. Destination inputs are strict and constrained to nullable Discord snowflake identifiers.

Resilience and Maintainability Implications

  • observed — A per-user advisory lock serializes command creation and rate-limit evaluation across instances. Unique identity includes user, hackathon, operation and idempotency key. Conflicting payloads are rejected, completed commands replay success, and more than five recent command starts causes transaction rollback. Pending and failed commands count toward the limit.
  • inferred — Interruption or delivery failure leaves a command retryable, and same-payload retries reuse its nonce. A successful Discord call followed by a failed completion write also leaves it retryable because that write error is swallowed. The submission limit bounds new command starts, not retry attempts; reliable duplicate suppression over delayed recovery therefore depends on provider nonce lifetime and scope, which the inspected source does not establish.

Hardening Proposals

  • proposed — Define the supported delivery-retry horizon against Discord's documented nonce guarantees. If recovery must extend beyond that horizon, add receipt reconciliation or explicitly document at-least-once delivery and bound repeated notification attempts. This is a proposal, not evidence of an observed exploit.
🚥 Pre-merge checks | ✅ 6 | ❌ 2

❌ Failed checks (2 warnings)

Check name Status Explanation Resolution
Docstring Coverage ⚠️ Warning Docstring coverage is 0.00% which is insufficient. The required threshold is 80.00%. Docstring coverage is scoped to functions touched by this diff. Analyzed 13 functions across 23 files. (6 skipped: … Write docstrings for the functions missing them to satisfy the coverage threshold.
Title check ⚠️ Warning The title describes the change but does not start with the required issue number in brackets. Use “[#595] Add hacker issue reporting”.
✅ Passed checks (6 passed)
Check name Status Explanation
Linked Issues check ✅ Passed Check skipped because no linked issues were found for this pull request.
Out of Scope Changes check ✅ Passed Check skipped because no linked issues were found for this pull request.
No Hardcoded Secrets ✅ Passed No hardcoded credentials were found in the PR additions. The credential-pattern scan found no matches in added lines. The token-like strings in existing tests are placeholder values, not secrets; the …
Validated Env Access ✅ Passed The PR adds no process.env usage. The only matches in changed files are existing lines in packages/api/src/tests/integration/hackathon-portal-configuration.test.ts; the diff does not modify them.
No Typescript Escape Hatches ✅ Passed The pull-request diff adds no any types, @ts-ignore or @ts-expect-error directives, or non-null assertions.
Description check ✅ Passed The description explains the issue-reporting change and its rate limit.
Full details: Docstring Coverage

Explanation

Docstring coverage is 0.00% which is insufficient. The required threshold is 80.00%. Docstring coverage is scoped to functions touched by this diff. Analyzed 13 functions across 23 files. (6 skipped: 6 unsupported.)

✨ Finishing Touches 💡 1
📝 Generate docstrings 💡
  • Commit to this branch
  • Create a new PR
🧪 Generate unit tests (beta)
  • Commit to this branch
  • Create a new PR

Thanks for using CodeRabbit! It's free for OSS, and your support helps us grow. If you like it, consider giving us a shout-out.

❤️ Share

Comment @coderabbitai help to get the list of available commands.

Co-authored-by: Codex <codex@openai.com>
@DVidal1205
DVidal1205 added this pull request to the merge queue Oct 5, 2026
Merged via the queue into main with commit 20dca5a Oct 5, 2026
14 checks passed
@DVidal1205
DVidal1205 deleted the 2026/hacker-issue-reporting-config branch October 5, 2026 22:18
Sign up for free to join this conversation on GitHub. Already have an account? Sign in to comment

Labels

None yet

Projects

None yet

Development

Successfully merging this pull request may close these issues.

2 participants